



Written by Bill Moore, CEO & Founder
TL;DR
- The Evolution of OT: Operational Technology (OT) emerged to monitor and control physical processes in environments like power plants and manufacturing, where uptime and safety are paramount.
- The Breakdown of the Air Gap: While traditional separation between IT and OT made sense, legitimate business needs for remote access, cloud analytics, and vendor support have dissolved the traditional air gap.
- The Need for Controlled Access: As operational systems connect to enterprise networks, security must shift away from rigid network boundaries toward an identity-based model that rigorously controls and monitors user and contractor sessions without slowing operations down.
In Part 1 of this series, I looked at how computing and telecommunications gradually became what we now call Enterprise IT. That change did not happen because someone decided to merge two departments. It happened because the technologies, the systems, and the work they supported became too interconnected to describe separately.
While that transformation was reshaping offices, finance teams, supply chains, and corporate networks, another technology revolution was unfolding in a different part of the enterprise.
It was happening in power plants, manufacturing facilities, water treatment plants, pipelines, transportation systems, and other environments where technology does not just process information. It helps operate physical processes.
That revolution became known as Operational Technology, or OT.
When Operations Became Digital
Historically, critical processes were operated locally and manually. Operators monitored gauges, adjusted controls, and worked directly with equipment on site. Automation gradually changed industries such as Energy, Utilities, Manufacturing and Transportation over time.
Programmable logic controllers, distributed control systems, remote terminal units, human-machine interfaces, and supervisory control and data acquisition systems brought computing into the heart of physical operations. A control room could monitor a process across a plant. A utility could view equipment across a service territory. An engineer could diagnose an issue without standing beside the asset.
Those systems were not built to run a corporate email system or manage payroll. Their job was to keep physical operations safe, reliable, and productive.
That distinction mattered. If an IT system went down, the consequences might be lost productivity or delayed business processes. If an operational system went down, the consequences could include a production outage, a power disruption, equipment damage, an environmental incident, or a safety event.
OT developed around that reality. Availability, safety, and operational continuity were not secondary concerns. They guided the functional processes of the business.
Operational continuity is the foundational priority of industrial environments, where system availability and physical safety always supersede traditional enterprise demands.
Why did the IT and OT divide make sense for industrial organizations?
For decades, keeping IT and OT separate was practical. They had different technologies, different owners, different risks, and often different physical locations.
IT teams managed business applications, enterprise networks, user devices, and data. OT teams managed industrial processes, control systems, engineering workstations, and equipment that could not simply be taken offline for an update.
The security models also reflected those differences. IT could often prioritize confidentiality and rapid patching. OT had to consider uptime, process safety, vendor support requirements, and the possibility that a well-intended change could interrupt a critical process.
Neither side was wrong. They solved different problems with the tools and priorities available to them.
The challenge is that industrial organizations no longer operate in the same environment they did when those boundaries were established.
Operational technology (OT) convergence is the ongoing integration of physical industrial processes with enterprise networks and cloud-based analytics.
How has connectivity changed the traditional OT operating model?
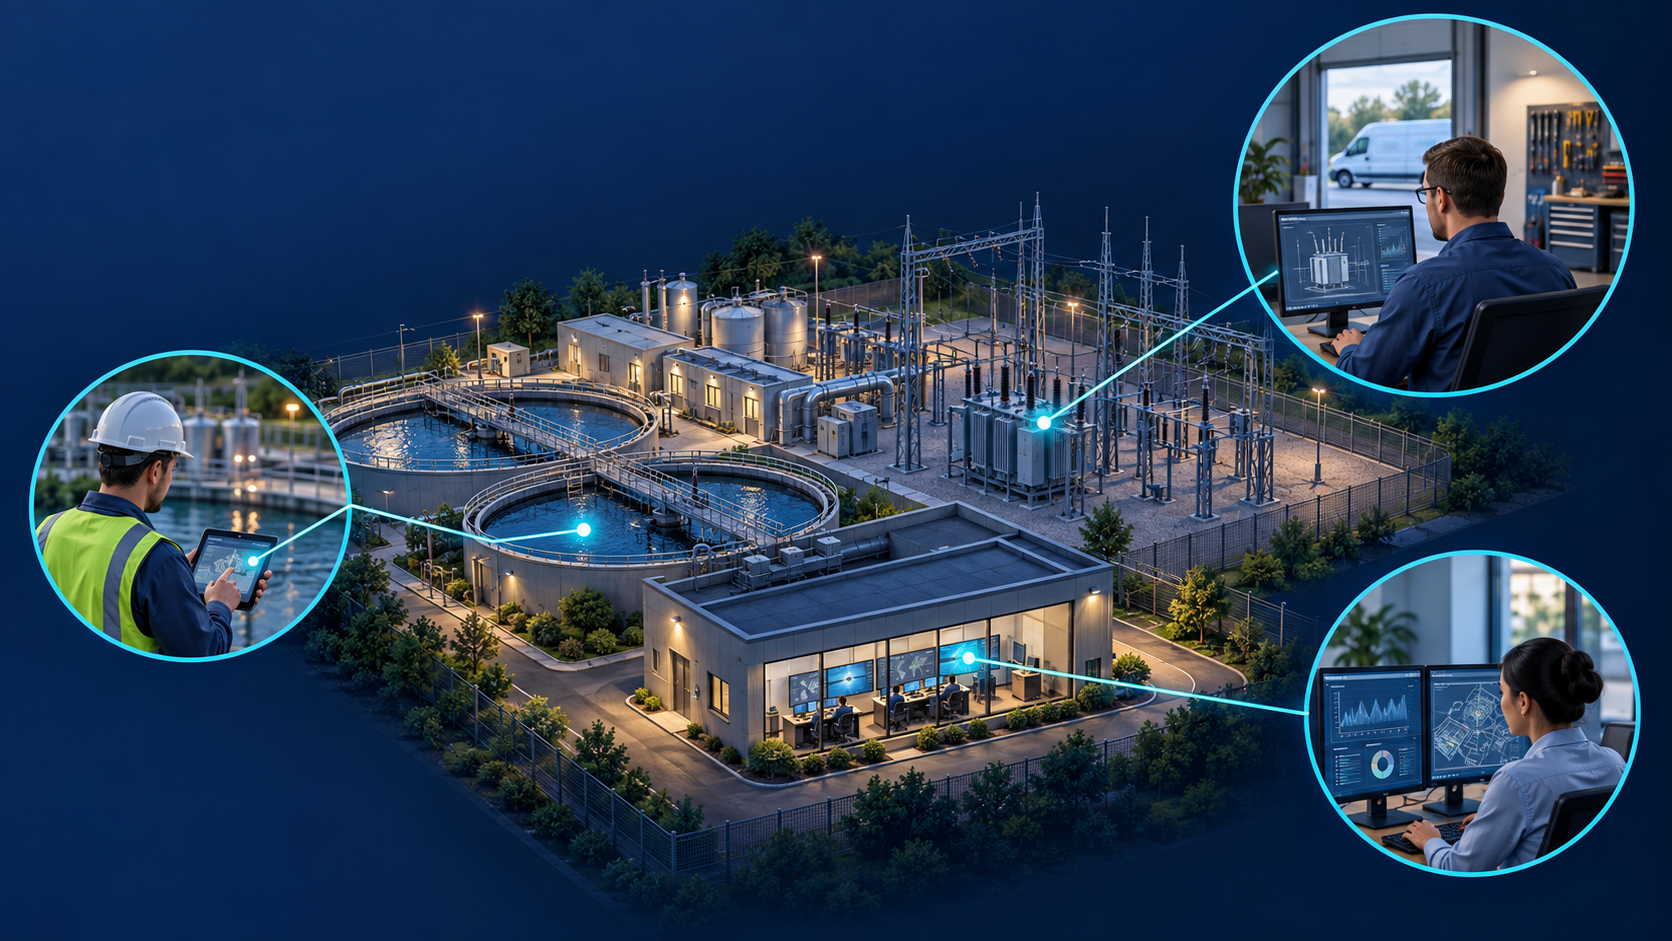
Industrial organizations connected their operational environments for good reasons. Remote access made it easier for specialists and vendors to support equipment. Enterprise systems gave leaders better visibility into operations. Cloud services made it possible to store and analyze large volumes of operational data. Connected sensors and applications helped teams identify issues earlier and manage assets more efficiently.
Those capabilities created real value. Utilities can respond more quickly to changing conditions. Manufacturers can reduce downtime. Water operators can identify potential problems before they become service interruptions. Energy companies can support widely distributed assets with fewer people on site.
But every new connection also changes the security question.
An engineering workstation that once communicated only within a facility may now need access to a vendor, a corporate identity system, a cloud application, or a remote support team. Operational data may feed enterprise dashboards and analytics platforms. Contractors may need temporary access to specific systems from outside the organization.
The air gap did not disappear in one dramatic moment. In many organizations, it gradually gave way to a set of legitimate business requirements.
Connectivity is not the problem. Uncontrolled connectivity is.
Who is responsible for security as IT and OT converge?
As IT and OT became more connected, the responsibility for protecting operations no longer belonged to one team alone.
An identity system may control access across enterprise and operational environments. A security team investigating a suspected incident may need to understand both business systems and industrial processes. An operations team may depend on an external vendor to resolve an issue quickly, while needing to limit that vendor to only the systems required for the task.
The question is no longer whether a system belongs to IT or OT. The more useful question is whether the organization can control, monitor, and account for access to the systems that matter.
That requires a security model that follows the user and the asset, not just the network boundary.
Operational access security utilizes a zero-trust modal which restricts users to only the specific assets and tasks they require, replacing perimeter trust with verified, identity-based controls.
A contractor should be able to reach the system they need, for the time they need it, without receiving broad access to an operational environment. Teams should be able to see who connected, what they accessed, and what occurred during a session.
Strong controls do not need to slow operations down. Done well, they make it easier to support remote work for both employees and the vendors supporting these connected systems that modern industrial organizations depend on.
More Than a Convergence Story
It would be easy to describe all of this as OT becoming IT. That misses the point.
Operational environments will always have requirements that are distinct from traditional enterprise systems. Safety, uptime, process integrity, and the realities of physical equipment do not disappear because a system is connected to the cloud or integrated with an enterprise platform.
What has changed is the degree to which operational decisions, business decisions, cybersecurity decisions, and technology decisions now depend on one another.
An industrial organization cannot modernize its operations without thinking about security. It cannot build a meaningful security strategy without understanding how people and systems interact with operations. It cannot make good business decisions without trustworthy operational data.
The old categories still describe parts of the environment. They no longer describe the whole of it.
What Comes Next
The first stages of this shift were digitizing operations and connecting systems. The next stage is about understanding what those connected systems can tell us.
Artificial intelligence is accelerating that change. It can analyze operational data, identify patterns, flag anomalies, and help teams make faster decisions. But intelligence is only as reliable as the systems and data behind it.
That makes secure, controlled access to operational systems paramount in the world of AI.
In Part 3, I will explore how AI changes the relationship between technology and operations, and why the next evolution is not simply about more information. It is about trusted operational intelligence.
Connect with the author: Follow Xona Founder and CEO Bill Moore on LinkedIn: https://www.linkedin.com/in/bmoore06/
This article is Part 2 of the Enterprise OIT Series. Catch up on Part 1: The Evolution of Enterprise IT.

